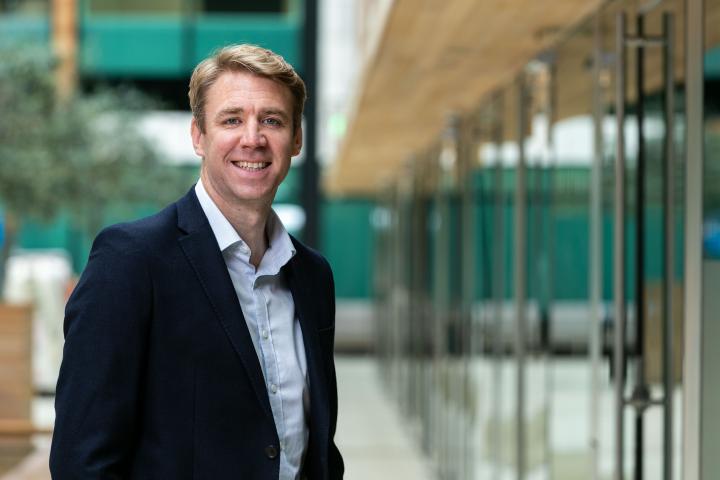
Comment from Richard Ford, CTO, Integrity360
“The Revolut incident is a reminder that organisations need to treat third parties as untrusted, regardless of how authoritative or legitimate a communication appears. Security awareness training also needs to focus on aspects of phishing that really matter, recognising how attackers use authority, urgency and context to make highly targeted requests feel credible. More importantly, strong verification processes shouldn’t stop at payments. Any request for sensitive data should be independently validated before information is released, even when it appears to come from a regulator, government agency or other trusted third party. For affected customers, the concern is that stolen personal information can have a very long shelf life, potentially enabling fraud and highly convincing phishing attacks long after the initial breach.”
Read the Summer 2026 edition free online →
Stay connected with NI's tech community: